Insider Risk Management
Transform endpoint activity signals into actionable risk intelligence. Correlate threat context, evaluate behavioral anomalies, and prevent data exfiltration before damage occurs.
Risk Intelligence Framework
Detect Threats with Full Operational Context
Replace point-in-time noise with multi-dimensional correlation across user, host, file, and application.
Composite Risk Scoring (0–100)
Every endpoint and user receives a normalized risk score calculated from policy infractions, unapproved peripheral writes, and sensitive data movements.
Behavioral Anomaly Baselines
Automatically flags deviations from peer group baselines, such as off-hours file staging, rapid archive compression, or sudden cloud storage upload spikes.
Forensic Investigation Timelines
Reconstruct what happened leading up to an incident with second-by-second chronological logs connecting applications, files, and external media.
Contextual Threat Correlation
Eliminate false positives by connecting disparate signals into a unified narrative—e.g. exporting customer records, archiving to ZIP, and inserting a USB drive.
Enterprise Forensic Search
Rapidly search across hostnames, user accounts, file names, hash signatures, and time windows to find evidence in seconds.
Automated Response & Triage Rules
Configure automated actions when high-risk events occur, including instantaneous USB lockdown, browser upload blocks, and SIEM alerting.
Alert Incident Center
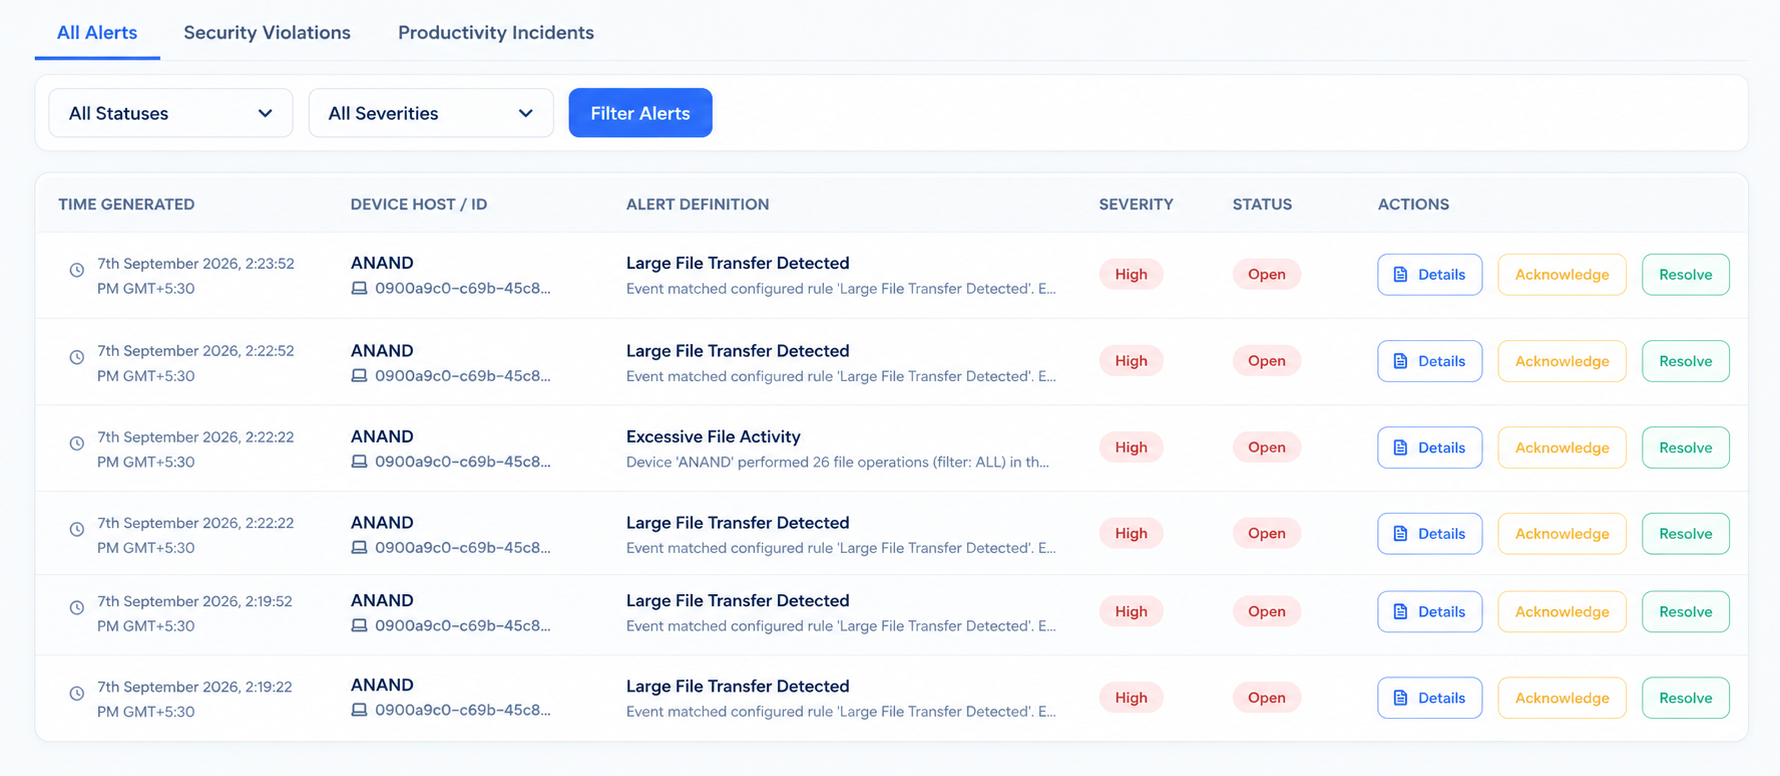
Sentinel correlates security policy violations, blocked websites, and USB events into a central incident triage queue. Security analysts can review affected users, device hostnames, risk score impact, and forensic timestamps with one click.
Detection Matrix
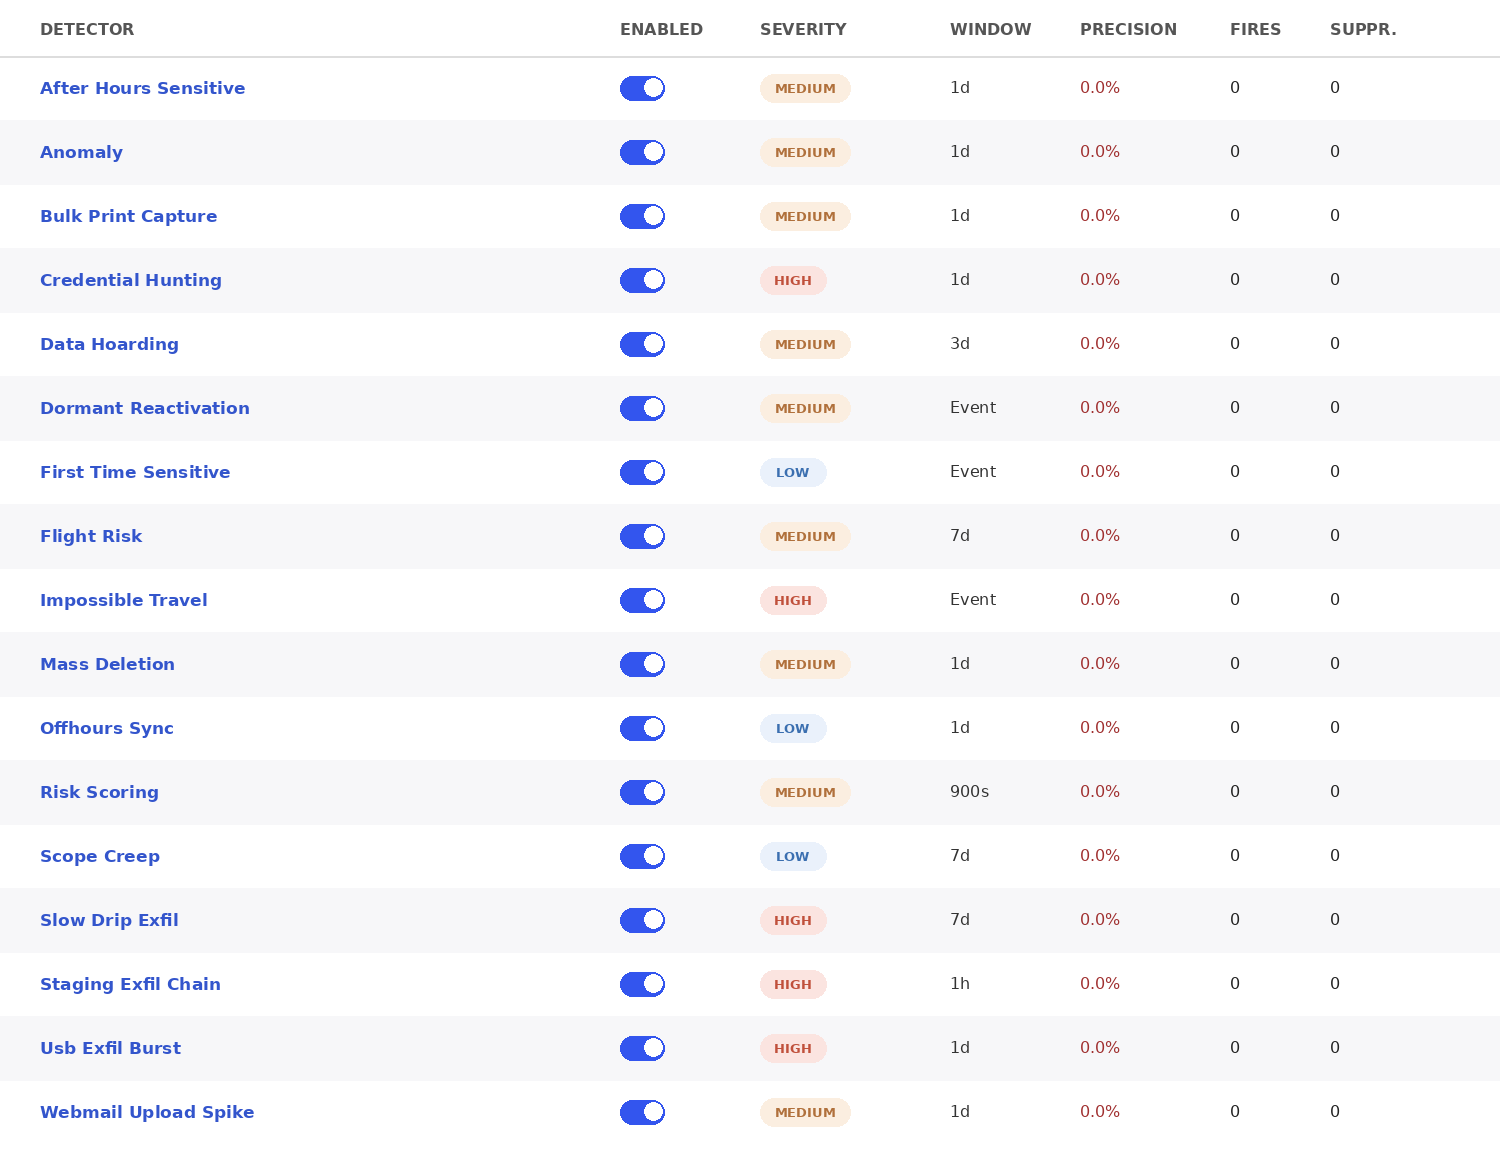
12 Real-Time Behavioral Threat Detectors
Continuous endpoint inspection covering USB exfiltration, credential hunting, off-hours spikes, flight-risk indicators, mass deletion, and webmail dumps.
Identify Insider Threats Before Data Leaves
Evaluate composite risk scoring and forensic investigation capabilities in your environment.