Endpoint Intelligence for the Modern Enterprise
See employee activity, endpoint behavior, sensitive data movement, and insider risk in one unified platform.
The Enterprise Challenge
Your endpoint data is fragmented.
Workforce activity lives in one system. Endpoint telemetry lives in another. Data-loss events appear somewhere else. Security teams are left connecting the dots manually.
Tracks active apps & hours in isolation, blind to sensitive data movement.
Logs hardware specs and OS events without employee or context awareness.
Generates disconnected upload alerts without historical user behavior context.
Analysts spend hours piecing disparate logs together after an incident occurs.
One Operational View
Sentinel connects users, devices, applications, files, and data movement into one unified operational plane. When a sensitive event occurs, security teams have immediate, complete context to investigate or act.
The Context Advantage
From Activity to Actionable Risk
A website visit alone tells you very little. A sensitive file copied to USB after unusual after-hours activity tells a very different story.
Isolated Alert: USB drive inserted on DESKTOP-A1B2. No user activity history or file sensitivity data attached.
Correlated Narrative: User accessed payroll export after scheduled shift hours, staged report.xlsx into a zip file, and attempted transfer to SanDisk USB. Risk score elevated to 88.
One Platform
One Platform. Four Layers of Visibility.
Sentinel connects workforce intelligence, endpoint monitoring, data protection, and insider risk into a single coherent architecture.
Workforce Intelligence
Understand application adoption, attendance verification, core working hours, and workload distribution patterns across distributed enterprise teams without invasive keylogging.
Endpoint Intelligence
Maintain continuous audit visibility across every workstation. Monitor hardware specifications, background processes, browser navigation history, and local file operations.
Data Protection & DLP
Safeguard intellectual property and confidential files. Enforce removable USB storage policies, scan local files for PII with PIIFindr, and restrict unapproved browser uploads.
Insider Risk Management
Surface elevated risk before security incidents escalate. Connect behavioral indicators, file staging, and data movement into chronological forensic timelines.
Operational Evidence
Enterprise Command & Control
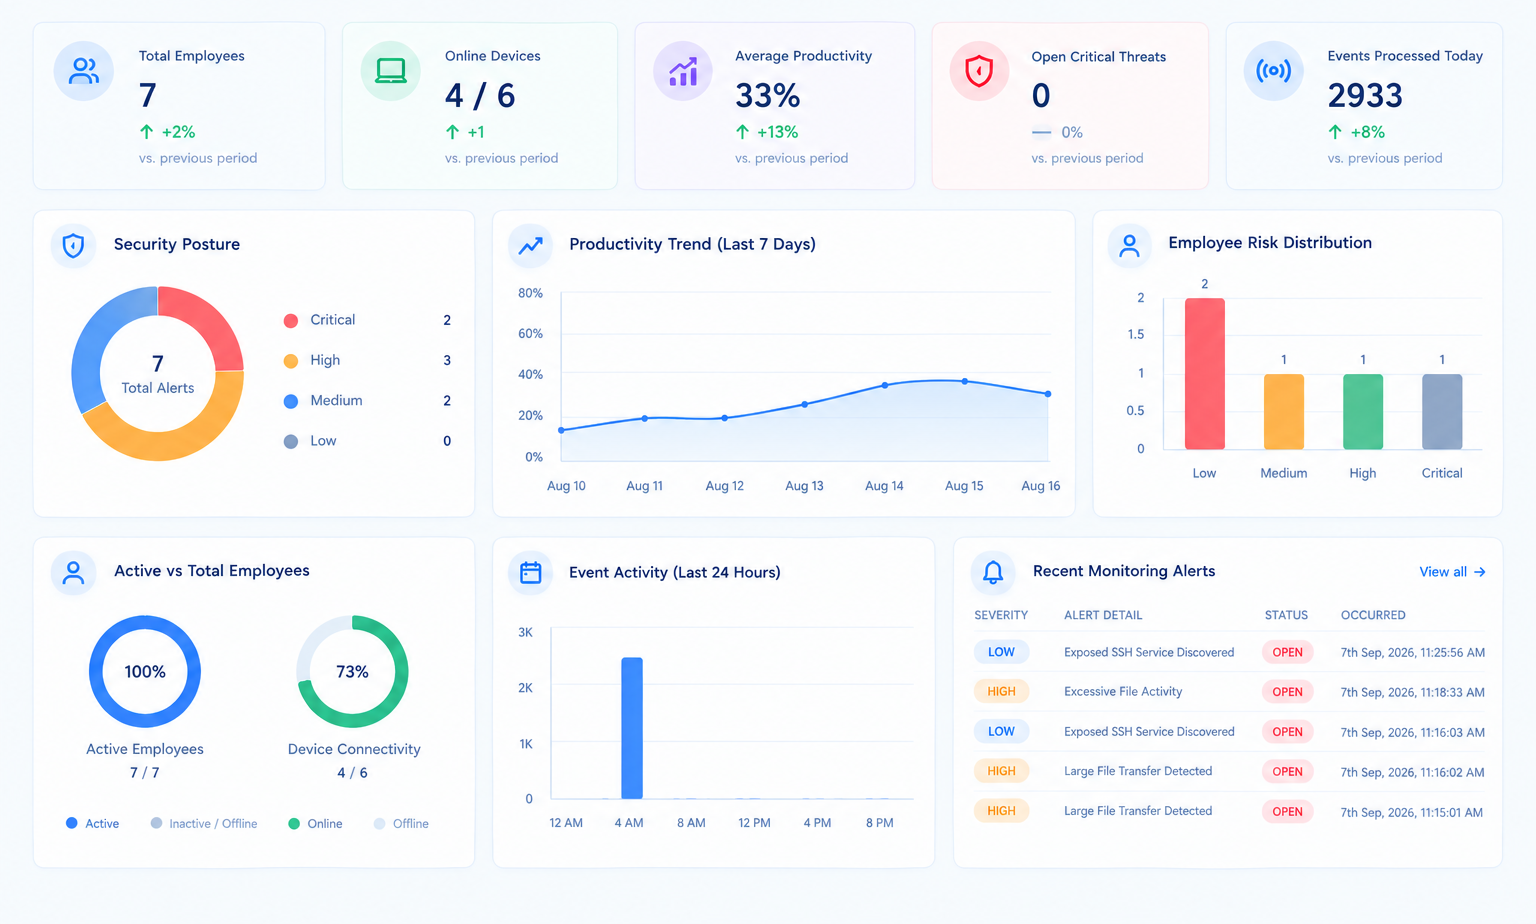
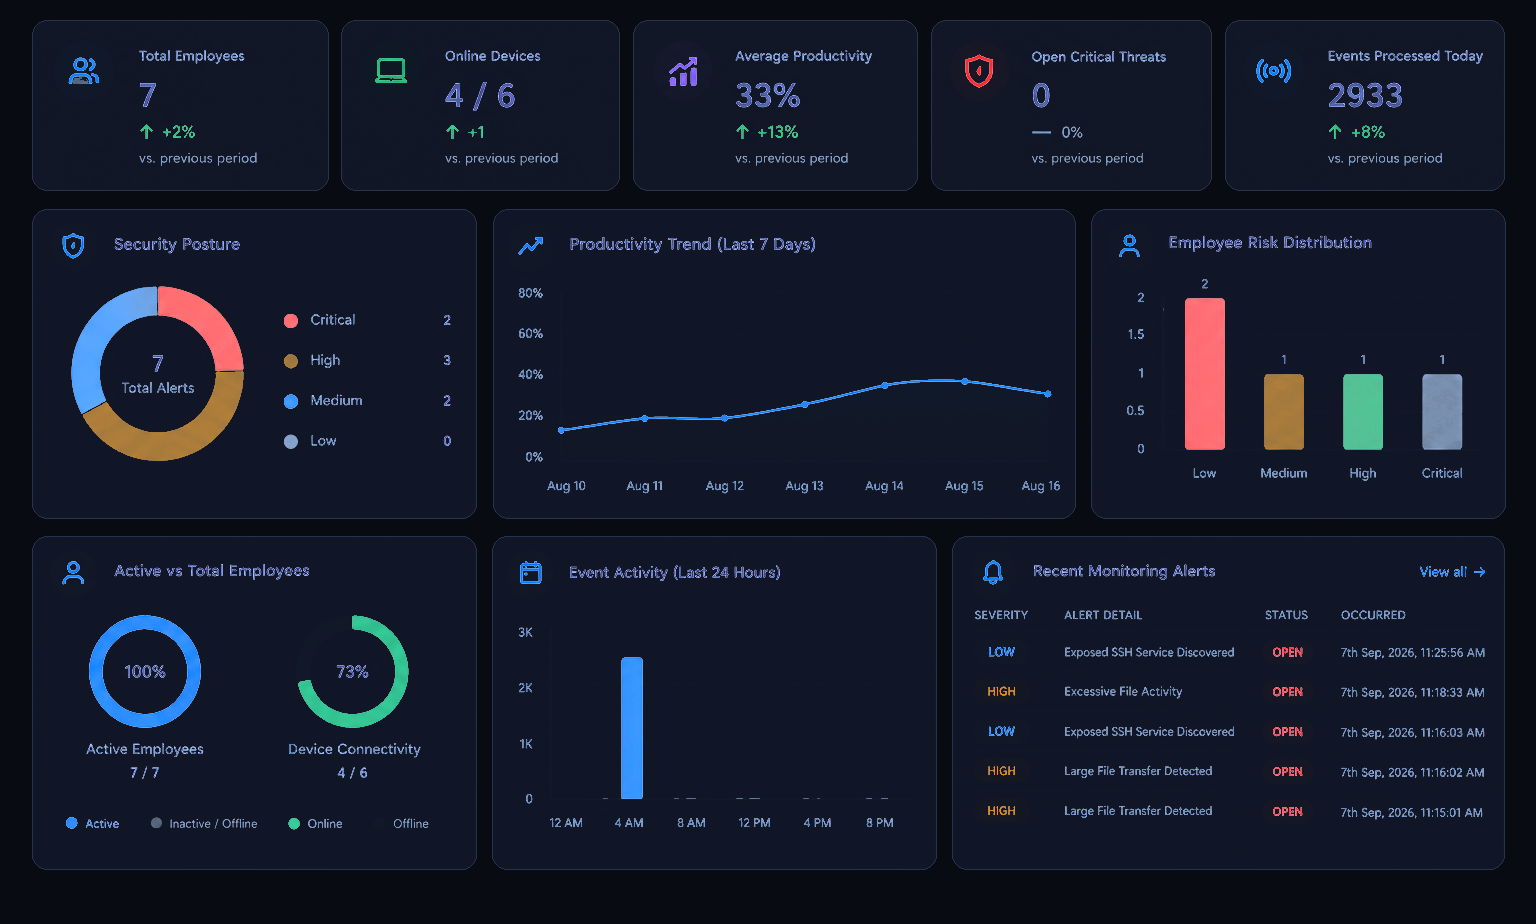
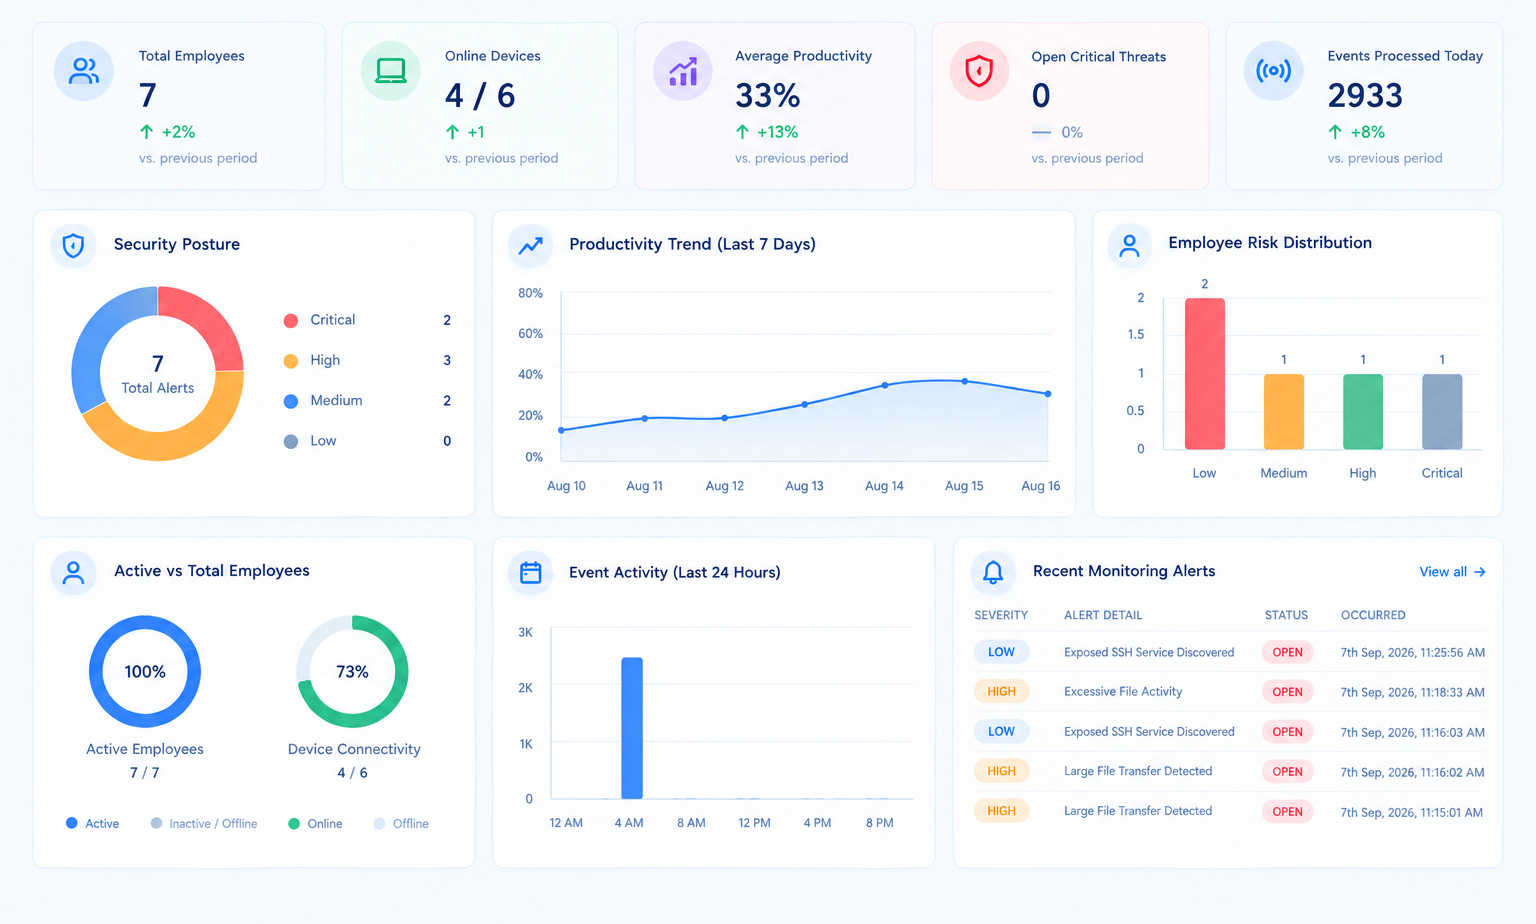
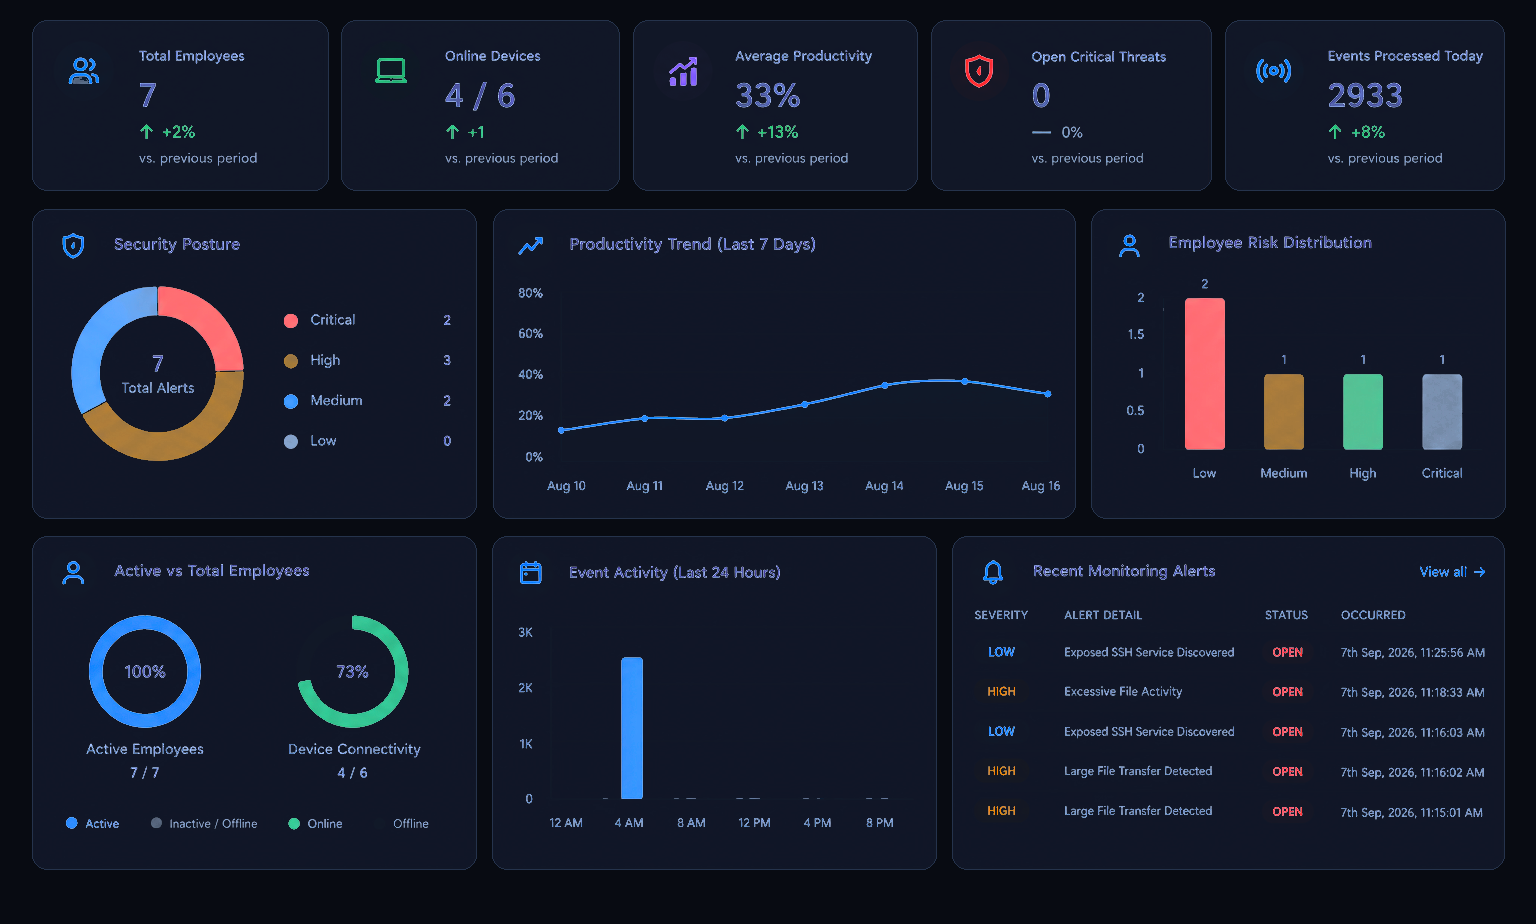
Real console screens demonstrating operational telemetry, incident management, and policy execution.
Company-Wide Operational Posture & Threats
Track active employees, online devices, threat posture, and 24-hour telemetry processing from an unified command interface.
Operational Scenarios
See Sentinel in Action
Realistic enterprise scenarios demonstrating how Sentinel surfaces threats and protects critical assets.
Prevent Data Exfiltration
Sensitive Record Access
Employee accesses proprietary customer records or financial exports.
Local File Staging
Files are saved to local disk or compressed into an archive.
USB Insertion Detected
Sentinel detects removable storage insertion, logging vendor and serial number.
Exfiltration Flagged & Blocked
Policy triggers immediate alert or enforces read-only storage lockdown.
Differentiation
Why Enterprises Choose Sentinel
One Agent
Workforce intelligence, endpoint telemetry, USB rules, and data protection through one lightweight native Rust agent.
One Data Layer
Connects users, endpoints, applications, files, and events into a single unified time-series schema.
One Risk View
Turns thousands of disparate endpoint telemetry events into prioritized, contextual incidents.
One Control Plane
Investigate, audit, alert, and enforce organization-wide policies from a centralized administrative console.
Enterprise Ready
Designed for centralized GPO/Intune mass deployment, RBAC access governance, and operational scale.
Trust & Transparency
Built for Security. Designed for Privacy.
Sentinel operates on a verified metadata-only contract. We believe enterprise security visibility should never compromise employee personal trust.
Approved Telemetry Collection
Collects application names, active window titles, browser domains, and file operation metadata strictly for security monitoring and operational analytics.
Metadata Only · No Raw ContentZero Invasive Snooping
Never records typed keystrokes, personal messages, passwords, or clipboard text. The agent ignores confidential credentials by architectural design.
Zero Keystroke RecordingCryptographic Safeguards
Strict TLS 1.3 encryption across all agent telemetry transit. Volume-level AES-256 database encryption and Windows DPAPI storage for device identity tokens.
TLS 1.3 · AES-256 · DPAPI TokensDeploy Across Your Organization in Hours
Sentinel packages standard Windows Installer (.msi) and setup binaries that integrate directly into existing endpoint management infrastructure.
Enterprise Stakeholders
One Platform. Dedicated Operational Value.
For IT & Infrastructure
Hardware inventory, background processes, device health audits, and silent mass rollout.
For Security Teams
Insider threat scoring, removable storage policies, PIIFindr scanner, and incident triage.
For HR & People Operations
Attendance verification, active vs. idle hours, workload balance, and non-intrusive activity logs.
For Compliance & Governance
Immutable audit logs, data protection governance, role-based controls, and exportable reports.
Commercial Packaging
Enterprise-Ready Capability Modules
Pricing is structured around endpoint volume, enabled capability modules, deployment requirements, and enterprise support needs.
Essentials
Workforce visibility & operational analytics.
- Shift attendance verification
- Active vs. idle duration analytics
- Standard executive dashboard
Professional
Workforce + endpoint fleet intelligence.
- Everything in Essentials
- Hardware & process inventory
- Browser domain & history tracking
Business
Endpoint intelligence + data protection + risk.
- Everything in Professional
- USB removable media policies
- Insider risk correlation engine
Enterprise
Full platform + DLP + dedicated SLA.
- Everything in Business
- PIIFindr sensitive scanner
- Dedicated deployment architect
Questions & Answers
Enterprise Buyer FAQs
See Everything Happening Across Your Endpoints
Bring workforce intelligence, endpoint visibility, data protection, and insider-risk detection into one unified platform.