Product Pillar
Data Protection & DLP
Protect sensitive corporate data wherever it moves. Enforce hardware USB policies, scan endpoints for unencrypted PII with native Rust, and intercept unauthorized browser uploads before leaks occur.
Data Loss Prevention Architecture
Defend the Three Critical Data Leakage Vectors
Physical removable media, unapproved browser uploads, and exposed local data-at-rest.
USB Storage Control & Peripheral Policies
Vulnerability:Employees can easily connect unauthorized personal USB sticks and exfiltrate confidential databases or source code.
Sentinel Control:Sentinel enforces hardware-level USB policies (Allow, Read-Only, or Full Block) via native Windows APIs in milliseconds.
Verified Capabilities
Instant USB read-only or block enforcement
Audit removable media serial numbers & vendors
Trigger forensic snapshots on mount events
PIIFindr Sensitive Data Scanner
Vulnerability:Unencrypted customer records, national IDs, and financial secrets sit forgotten in Downloads and Desktop directories.
Sentinel Control:Native Rust crate scans local drives with regex heuristics and checksum validation (Aadhaar, PAN, SSN, Credit Cards, API keys).
Verified Capabilities
Pre-configured PII & financial checksum rules
Custom enterprise keyword & pattern definitions
Discovers exposed secrets across local volumes
Browser Data Loss Prevention (DLP)
Vulnerability:Employees accidentally or deliberately upload internal spreadsheets to personal webmail or generative AI tools.
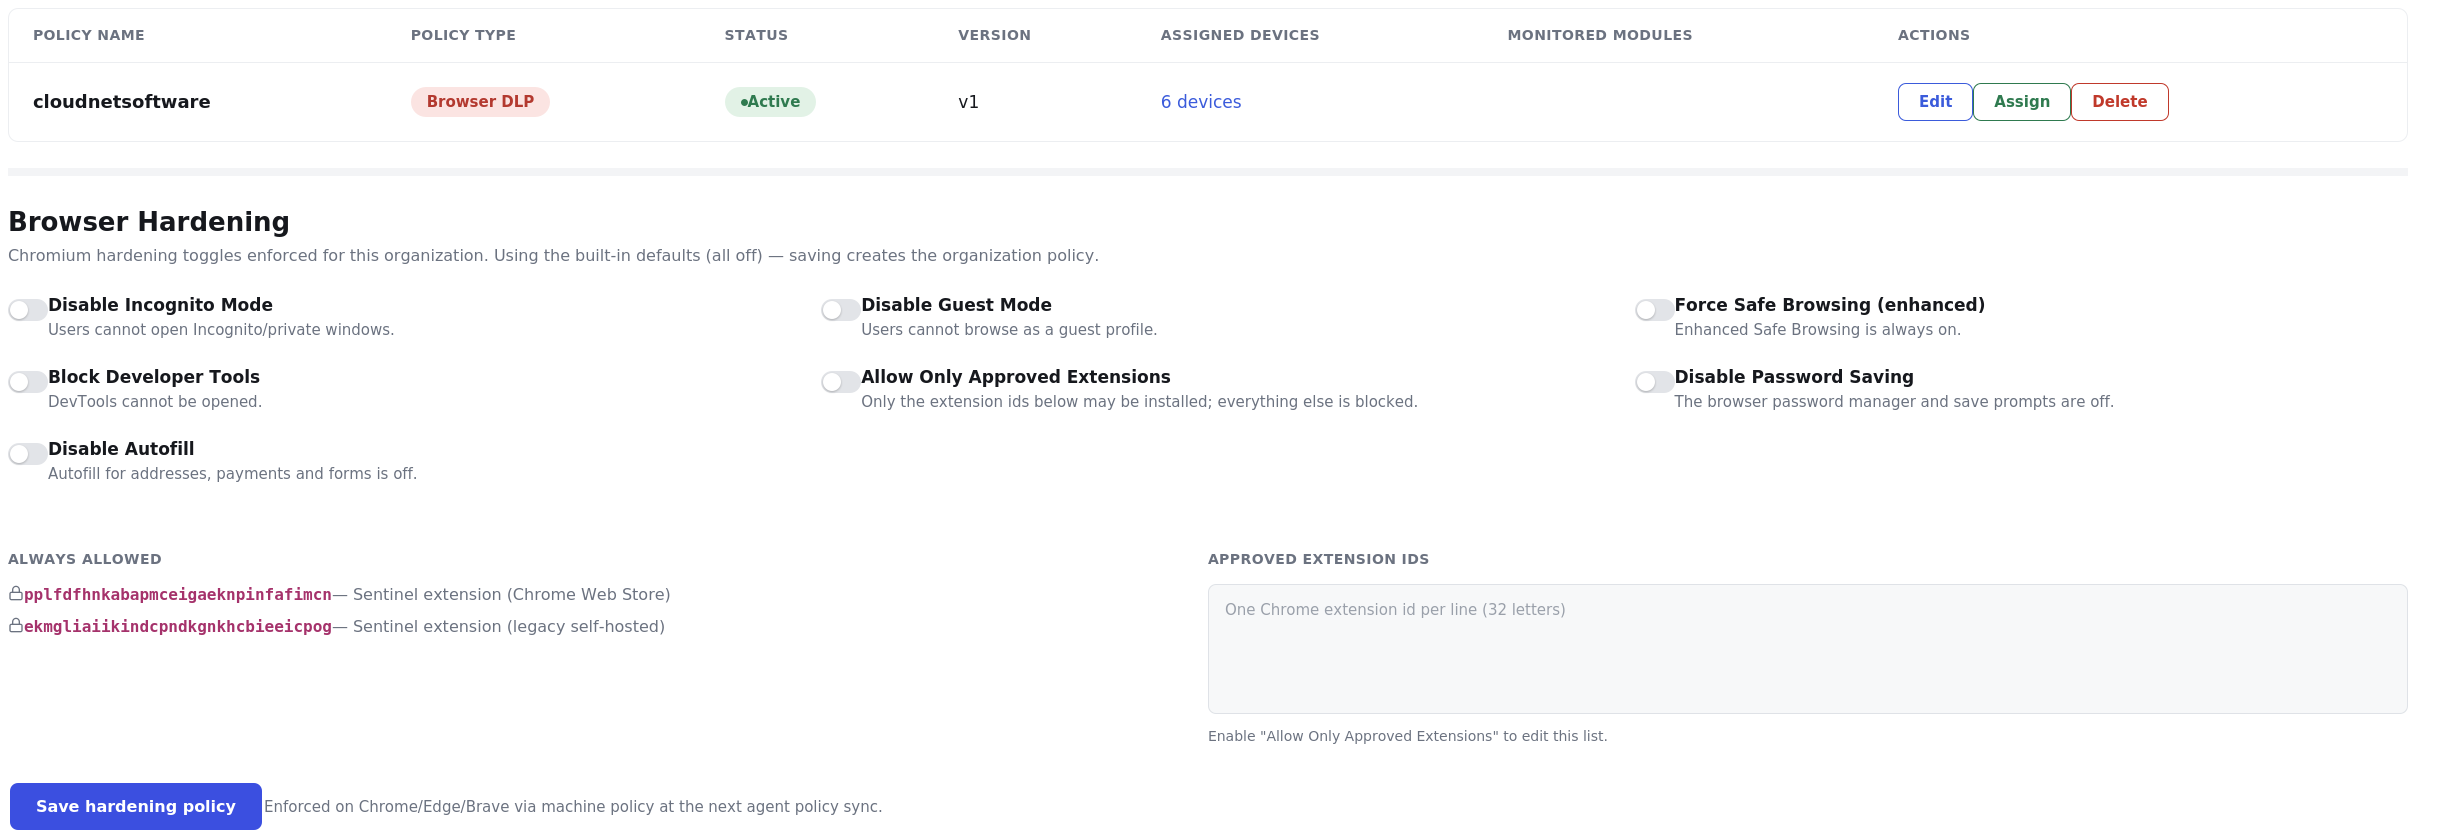
Sentinel Control:Manifest V3 companion extension bridges to the native agent, intercepting file uploads and blocking unapproved domains.
Verified Capabilities
Monitors web file uploads & attachments
Blocks unapproved cloud storage & pastebins
Inspects destination URLs and file metadata
File Activity & Movement Tracking
Vulnerability:Ransomware preparation or data theft often involves mass file compression, renaming, and rapid staging before exfiltration.
Sentinel Control:Sentinel monitors file lifecycle events across corporate folders, flagging rapid mutations and ZIP archive creation.
Verified Capabilities
Tracks PDF, DOCX, ZIP, CSV, SQL files
Detects mass file compression & rapid downloads
Chronological file interaction breadcrumb trail
Real-Time Exfiltration Alerts
Vulnerability:Security analysts discover data breaches weeks or months after an insider has already transferred sensitive assets.
Sentinel Control:The platform evaluates endpoint events against DLP policies, triggering high-severity alerts within seconds of a violation.
Verified Capabilities
Sub-second alert center notifications
Configurable email and webhook dispatch to SIEM
Composite risk scoring from 0 to 100
Tamper-Resistant Native Agent
Vulnerability:Savvy users kill background monitoring processes or uninstall security tools to bypass data protection rules.
Sentinel Control:Running as a protected Windows Service with administrative ACLs, DPAPI storage, and local offline database buffering.
Verified Capabilities
Service self-defense with Windows ACLs
Encrypted local SQLite queue (events.db)
Continuous binary SHA-256 integrity checks
Production Console
Granular Policy Enforcement in Action
Real screenshots from the live Sentinel management interface.
Chromium Browser Hardening Policy Consolesentinel://dlp/browser-hardening
Protect Enterprise Intellectual Property
Discover exposed sensitive data and stop unauthorized exfiltration with a lightweight, non-kernel architecture.